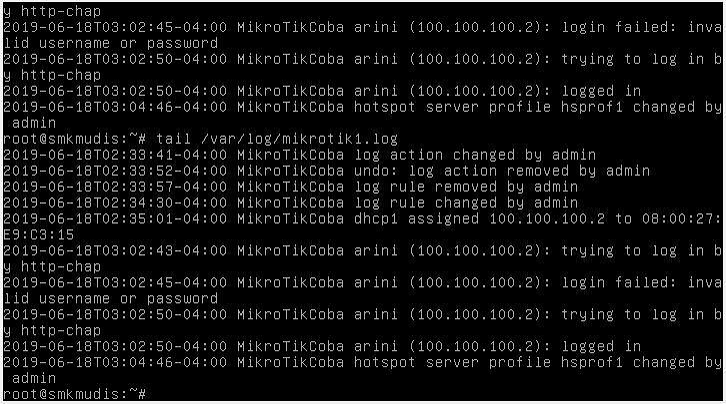
Cloutik shows you, in real time, what your RouterOS devices report day to day: the Critical, Warning and Info topics. By design, it does not collect everything a router can send. When you need the full history, with every login and every firewall hit kept for months, the logs have to go to a remote log server. Here is how to set that up without touching your Cloutik configuration.
Why the router alone is not enough
y default, RouterOS keeps its last 1,000 log lines in memory, and loses them at reboot. That is enough to troubleshoot what is happening now, not to answer questions like these:
- Who logged in to this router last month, through Winbox, SSH or the web interface?
- Which device was on the Wi-Fi of this site on a given evening?
- Which firewall rule has been dropping this traffic, and since when?
What to send
Three topics cover day-to-day operations: info, warning and error. Firewall rules only produce log lines when they have log=yes. Add a log-prefix so you can recognise each rule in the logs.
Sending logs to a remote server, alongside Cloutik
RouterOS can send its log to several destinations at once. Your Cloutik configuration stays as it is: you add a second logging action. Over UDP, it takes four lines in a RouterOS terminal:/system logging action add name=remotelog target=remote remote=SERVER_IP remote-port=514
/system logging add action=remotelog topics=info
/system logging add action=remotelog topics=warning
/system logging add action=remotelog topics=error
Replace the address and port with those of your log server.
Choosing the transport
UDP works on every RouterOS version: one message per packet, nothing else to set on the router. It is not encrypted, and a lost packet is not resent.
TCP has a trap. In the default and syslog formats, RouterOS writes its messages one after another in the stream, with nothing between them, so the server cannot tell where one ends. Use the CEF format with an explicit delimiter, on RouterOS 7.18 or later. Type the command in a terminal: the WinBox form reads \n as two characters.
/system logging action add name=remotelog target=remote remote=SERVER_IP remote-port=PORT remote-protocol=tcp remote-log-format=cef cef-event-delimiter="\n"
Check that your log server reads CEF.
TLS encrypts the same stream, on RouterOS 7.25 or later. Import your server’s certificate authority with trusted=yes, and set check-certificate=yes. Without it, RouterOS encrypts without checking who it is talking to.
No fixed public address? A router on 4G, or with a changing IP, can send its logs through a WireGuard tunnel on RouterOS 7. The logs travel encrypted, and the server recognises the router by its key rather than its address.
In France and French-speaking countries
Infralogs, a Cloutik partner, does all of the above as a service hosted in France. It receives RouterOS logs over UDP, TCP, TLS or a WireGuard tunnel, and keeps them for 12 months. It flags an account that gets in after a series of failures, or a router that goes silent, and shows a whole fleet on one screen. The details are on its MikroTik RouterOS page. The demo is free for 30 days, with no credit card. The interface is in French for now; other languages are planned.
In France, operators of public Wi-Fi, such as hotels, campsites and town halls, must also keep connection data for one year.